Blogmark
On "Preventing Paste for a 'Destructive Action' Confirmation Input"
via jbranchaud@gmail.com
A general principle I have is that you shouldn't ever (I'm sure there are some rare, specialized caveats) prevent someone from pasting into a text area in a web app. Financial/IRS forms sometimes like to prevent you from pasting the "Account number confirmation" or "Routing number confirmation" field. Don't do that. I'm directly copying it from my bank website, I don't need you to force me to type it out to somehow "prevent" a mistake.
Same principle here. Don't disable paste on a text field even if it is a field meant to slow you down on an irreversible or destructive action. There are better UX solutions to reach for if you are worried about people automating the "danger zone" field. E.g.
- have a 5s delay where the person can click 'undo' if it was a mistake
- implement a soft-delete system that archives for now and fully deletes in 30 days
Here is an example of GitHub requiring you type the qualified name of the repository to confirm that you want to transfer ownership.
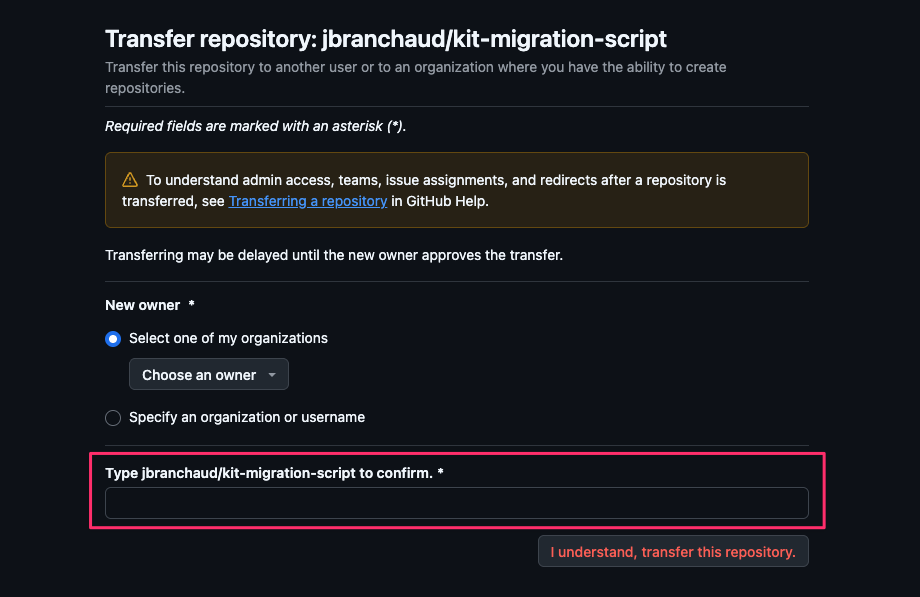
Notably, they don't prevent you from pasting.
I see this confirmations as making destructive actions cat-proof (you know, when a cat walks on your laptop keyboard and trackpad), not script-proof. Scripts can easily get around the paste restriction anyway. All you're doing when preventing paste is adding extra UI logic to make your UX worse.